For a small business in Brea, the cost of a data breach can vary widely. The final bill depends on what data is exposed, how long systems are disrupted, and how quickly the business contains the incident.
That uncertainty makes planning difficult, especially because recovery costs go beyond the initial technical fix. This guide explains the expenses that can add up, the threats small and medium-sized businesses face, and how average breach-cost figures can help set expectations. It also covers practical steps to limit disruption and support a more organized response.
Key Takeaways
- Estimate breach costs beyond technical recovery: downtime, investigation, restoring data, and customer impact can all add to the bill.
- See why delays matter. The longer a breach takes to identify and contain, the more time and resources recovery can demand.
- Learn how cybersecurity, managed IT, and cloud services can support prevention and a more organized response.
What does a data breach cost a small business?
The cost of a data breach for an SMB in Brea depends on the data involved, the industry, and recovery time. These figures cover organizations of different sizes, so they provide context, not a local estimate.
Industry matters, too. A single figure cannot capture every operational impact. Phishing and software exploits can trigger very different recovery needs.
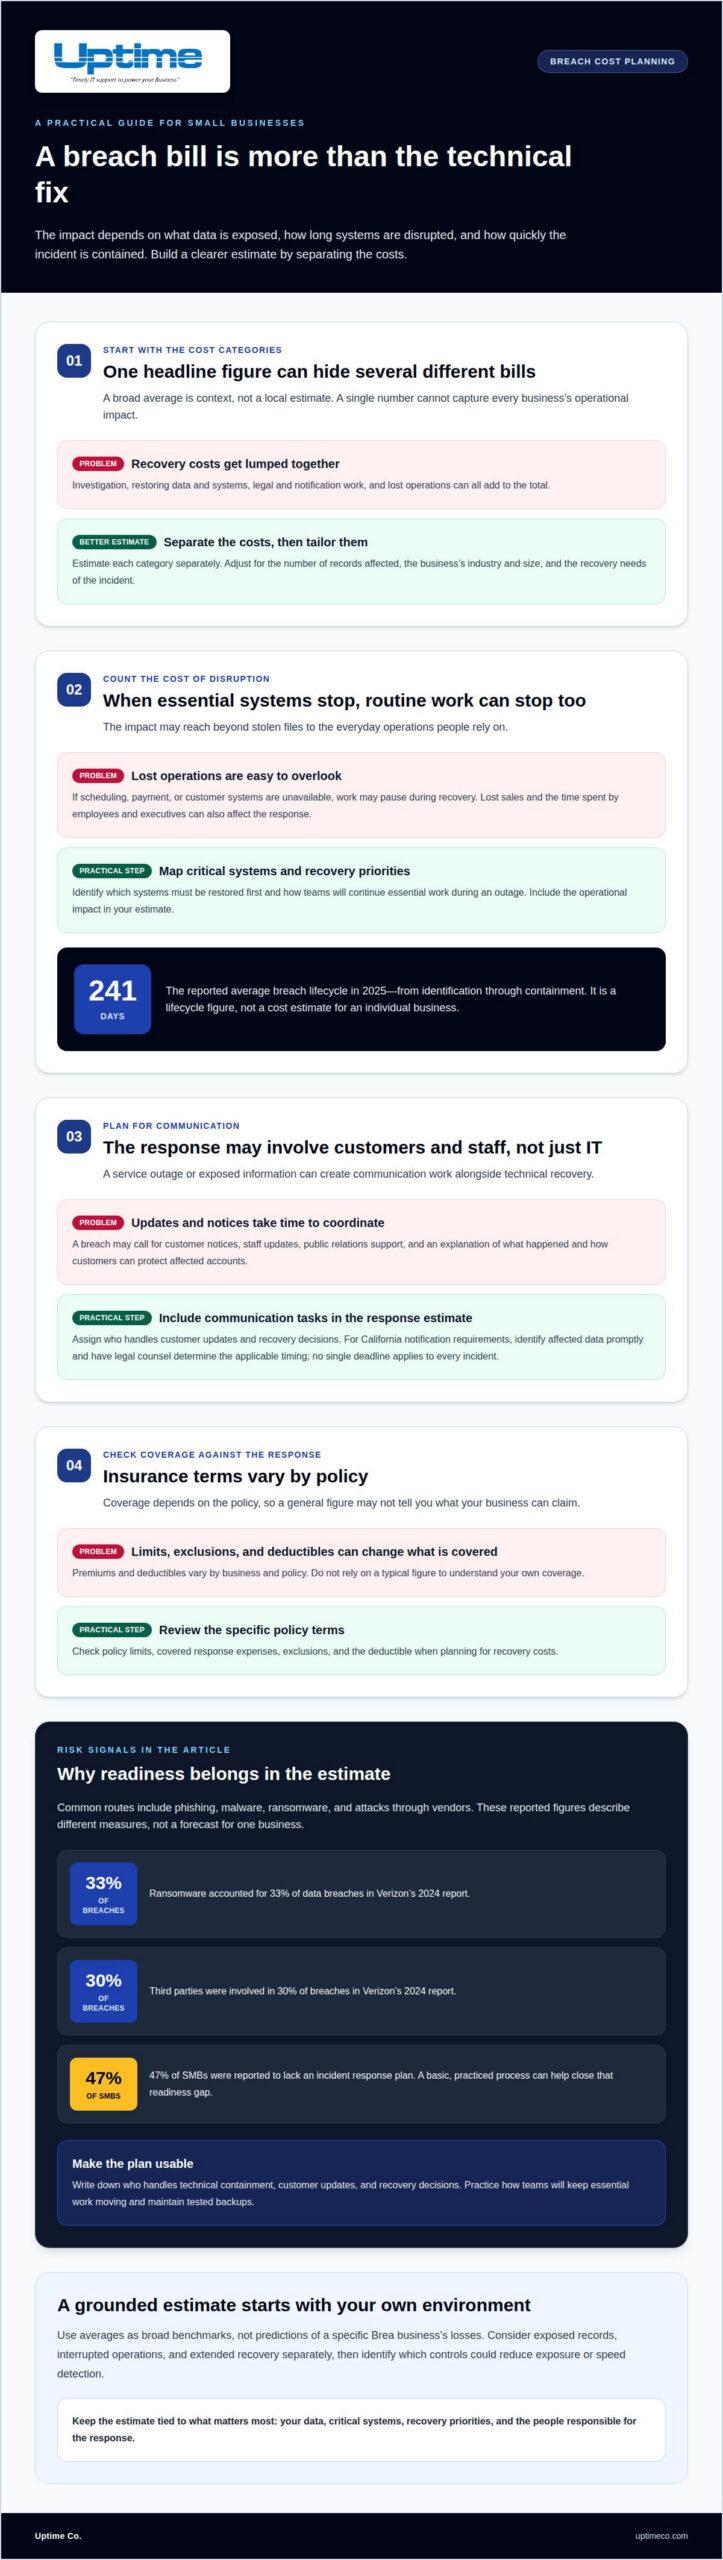
Prevention spending and incident recovery are not directly comparable. Prevention supports cybersecurity before an attack, while response costs depend on what happened. For a useful estimate, separate investigation, system restoration, legal and notification work, and lost operations. Then tailor it to the number of records affected and the business’s industry and size.
Cyber insurance coverage depends on policy limits, covered response expenses, exclusions, and the deductible. Premiums and deductibles vary by business and policy, so review the specific terms rather than relying on a typical figure.
Don’t overlook communications. A breach may require customer notices, staff updates, and public relations support. For example, a business facing service outages may need to explain what happened and how customers can protect affected accounts. Include these tasks, along with executive and employee time, in your response estimate.
Cybersecurity risks for small and medium-sized businesses
A small business can be a target even without a large customer database. Verizon’s 2023 Data Breach Investigations Report found SMBs suffered more breaches than large organizations. Common routes include phishing, malware, ransomware, and attacks through vendors. A compromised employee login can expose customer records or interrupt essential systems. The financial impact can spread from recovery work to lost sales and reputation damage. These risks shape the cost of a data breach for an SMB in Brea, too.
Ransomware accounted for 33% of data breaches in Verizon’s 2024 report, and third parties were involved in 30% of breaches. In California, Wood Ranch Medical closed after ransomware encrypted access to critical patient records and blocked backup systems. That example shows why continuous access to usable backups and clear recovery steps matter. Implement controls such as staff phishing awareness, restricted account access, and tested backups. For Brea businesses, these practices also help make local response plans more practical.
California breach notification requirements depend on the information exposed and the circumstances. No single deadline applies to every incident. Identify affected data promptly, escalate the decision, and have legal counsel determine the applicable notification timing.
The operational risk is broader than stolen files. If employees can’t reach scheduling, payment, or customer systems, routine work may stop while recovery proceeds. The reported average breach lifecycle was 241 days in 2025, from identification through containment. Map critical systems and decide how teams will continue essential work during an outage, especially for business-to-business transactions and workflows handled through 123 EDI.
Use a written response plan to assign who handles technical containment, customer updates, and recovery decisions. Since 47% of SMBs were reported to lack an incident response plan, even a basic, practiced process can help close a readiness gap. Strengthen those cybersecurity controls before an attack forces rushed decisions.
Average SMB data breach cost
There is no universal average for a small-business breach in the United States. Treat any average as a broad benchmark, not a bill every smaller company should expect.
Other estimates use different samples and definitions. The range reflects how the target, exposed data, operational disruption, and recovery needs can change the damage. Malware affecting one device calls for a different response than an attack that shuts down core systems or exposes customer records.
The time an incident takes to detect and contain can significantly affect the impact. Delayed monitoring can leave vulnerabilities open longer. External access, complex systems, and slow coordination can also complicate containment. Security teams can use this insight to set clear escalation steps and maintain continuous monitoring.
Compare averages carefully. Neither predicts a specific Brea business’s losses. Use them to frame scenarios by estimating the impact of exposed records, interrupted operations, and extended recovery separately. Then identify which controls could reduce exposure or speed detection.
Build a practical response plan around your systems, data, and recovery priorities. Strengthen your cybersecurity readiness before an incident puts those decisions under pressure.
Uptime
Uptime Co. helps Brea businesses connect breach-cost planning with practical IT and cybersecurity decisions. Its Managed IT Services and Cybersecurity Solutions can help clarify systems, risks, and response priorities. Cloud Services and Network Infrastructure can also inform business continuity and recovery planning.
Turn to Uptime Co. when mapping critical systems, reviewing security gaps, or shaping a response plan. Start by identifying the data and operations your business needs to restore first. This grounds planning in your actual environment rather than broad industry averages.
Contact Uptime Co. to discuss your business’s IT and cybersecurity needs.
Turn breach planning into your next practical step
Planning for the cost of a data breach for an SMB in Brea starts with a decision you can make now: identify which systems must stay available and who leads if an incident disrupts them. Put those priorities into a response plan, then align security controls, backups, and communication steps around them. Clear ownership makes preparation part of routine work, not a scramble. Revisit the plan as your systems and business needs change.
Uptime offers Managed IT Services, Cybersecurity Solutions, and Cloud Services to support businesses as they address IT and security needs. Start with the gaps that matter most to your operations, whether that means clarifying responsibilities or strengthening protection for critical systems. Talk with Uptime about your security needs and consider a practical next step for your business. A clearer plan can help you move forward with focus and confidence.
Frequently Asked Questions
What Costs Should You Expect After a Breach?
Expect both new invoices and costs hidden in ordinary business operations. Keep a separate incident ledger for outside specialists, legal review, temporary workflows, and staff time. Record when each expense begins and which business function it supports. This helps distinguish immediate response spending from longer-term effects and gives insurers or accounting teams clearer documentation when reviewing the incident.
What are typical data breach costs for SMBs by company size and industry?
There is no single typical cost that applies to every SMB. Company size matters, as do the type of information held, system complexity, and how much the business depends on affected systems. For example, a small accounting firm handling sensitive client files faces different recovery tasks from a retailer whose payment systems are interrupted. Compare estimates only when their samples and cost definitions match.
How much does breach response, investigation, and forensic analysis cost for a small business?
Incident response costs can exceed $100,000 depending on the breach’s extent. Forensic work may involve tracing how access began, identifying affected systems, preserving evidence, and confirming containment. Costs depend on the investigation’s scope and the time specialists need. Track response hours and deliverables separately, so you can see which work addressed the cause and which supported recovery.
What are the average costs of customer notification, credit monitoring, and call-center services after a breach?
These costs depend on how many people need notice, what contact details are available, and how much support customers need. Credit monitoring adds a separate per-person service expense, while a call center’s workload depends on inquiries and call volume. Build estimates using affected-record counts, communication channels, support hours, and how long services must remain active.
What are the legal fees, regulatory fines, and settlement costs for an SMB data breach in California?
Legal and settlement expenses depend on the information involved, claims made, and work needed to respond. The California Legislature states that intentional CCPA violations can incur fines of $7,500 per incident. That figure applies to intentional violations, not every breach. Keep legal defense, regulatory penalties, and any settlement in separate budget categories, since each has different triggers and documentation.